
Key Takeaways
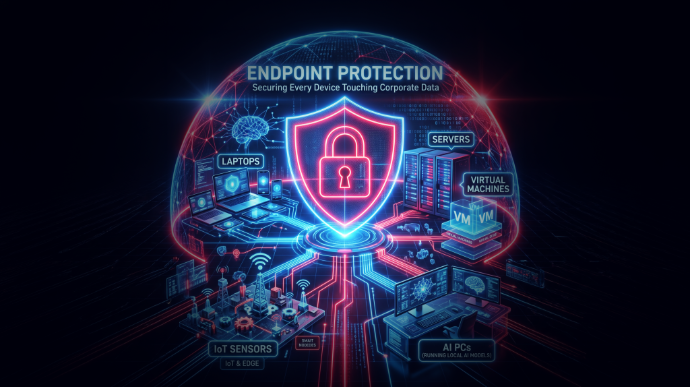
- Endpoint protection covers every device that touches corporate data, from laptops and servers to virtual machines, IoT sensors and AI PCs running local models.
- An endpoint protection platform (EPP) blocks threats before they run, while endpoint detection and response (EDR) records activity to catch and contain attacks that get through.
- Endpoint security is the broader program; EPP, unified endpoint management (UEM) tools such as Microsoft Intune, and endpoint backup each cover a different layer.
- Wiping a lost or compromised device protects the organization, but it does not restore the OneDrive, SharePoint or Teams files the user was working on.
- On-device AI assistants and agents act with user or non-human identities, so they expand the endpoint attack surface and need identity, configuration and recovery controls.
Every laptop, phone, server and virtual machine that signs in to corporate systems is a potential entry point for attackers. Endpoint protection is the set of tools and controls that keeps those devices secure, compliant and recoverable. This guide explains how endpoint protection works, how EPP compares with EDR and antivirus, how it applies to Microsoft 365 and Intune, and what changes as AI agents move onto the device.
What Is Endpoint Protection?
Endpoint protection is the practice of securing end-user devices and servers that connect to an organization's network against malware, ransomware, exploits and unauthorized access. An endpoint protection platform (EPP) delivers this capability, typically through a lightweight agent installed on each device and a central console that sets policy, collects telemetry and reports device status.
Modern endpoint protection goes beyond signature-based scanning. It combines next-generation antivirus, behavioral analysis, exploit prevention, device encryption, application control and integration with identity systems, so access decisions reflect device health. Because most work data now lives in cloud services and syncs to the device, the endpoint is where identity, data and applications converge. That makes endpoint protection a core part of any cybersecurity program.
What Counts As An Endpoint, Including AI PCs
An endpoint is any device that runs code and communicates with the corporate network or cloud services. Common categories include:
- Desktops and laptops running Windows, macOS or Linux
- Smartphones and tablets, both corporate-owned and bring your own device (BYOD)
- Physical servers, virtual machines and cloud workloads
- Point-of-sale terminals, IoT sensors and operational technology
- AI PCs with neural processing units (NPUs) that run language models and AI assistants locally
The last category is new. An AI PC can process prompts, files and screen content on the device, so sensitive data may be handled by local models outside the view of cloud-based controls.
Endpoint Protection Vs. Endpoint Security Vs. Antivirus
The terms overlap, but they are not interchangeable. Antivirus is the oldest layer: it compares files against known malware signatures and quarantines matches. Endpoint protection is a platform that includes antivirus plus behavioral detection, exploit blocking, firewall and device control. Endpoint security is the broadest term, covering the full program of tools, policies and processes, including EDR, UEM, patching, encryption and endpoint backup.
Why Endpoint Security Matters Now
Endpoints Are The Front Door To Cloud Identity
Hybrid work moved the security perimeter to the device. Users sign in to Microsoft 365, Google Workspace and Salesforce from home networks, personal phones and shared machines. A single compromised device can expose session tokens and cached credentials for every service the user can reach, which is why endpoint controls and identity and access management must work together.
Threat data confirms the pattern. Phishing was the dominant intrusion vector in roughly 60% of the incidents analyzed by the European Union Agency for Cybersecurity, and vulnerability exploitation accounted for 21.3% of initial access, according to the ENISA Threat Landscape 2025 report. Both vectors typically land on an endpoint first.
Unmanaged Devices And Infostealer Malware
Credential theft often starts with infostealer malware on a device the security team does not manage. Verizon's 2025 Data Breach Investigations Report found that 30% of compromised systems in infostealer credential logs were enterprise-licensed devices, while 46% of systems holding corporate logins were non-managed devices. Endpoint protection that stops at company-owned laptops leaves a large share of real exposure uncovered.
How Endpoint Protection Works: The Three-Layer Model
Most endpoint security guidance focuses only on stopping attacks. A complete endpoint protection strategy has three layers, and each answers a different operational question.
Layer 1: Prevent And Detect With EPP And EDR
The first layer blocks and investigates threats. EPP prevents malware, fileless attacks and exploits before they run. EDR continuously records process, file, registry and network activity so analysts can detect suspicious behavior, trace the root cause and isolate a device from the network.
Layer 2: Configure And Prove Device Compliance
The second layer keeps devices configured the way policy requires. This includes encryption with BitLocker or FileVault, operating system and application patch levels, firewall settings, compliance baselines and conditional access rules. Security teams also need evidence: reports that show which devices met the baseline, which drifted and when each issue was corrected. Auditors and regulators increasingly ask for this proof, not just a written policy.
Layer 3: Recover With Endpoint Backup
The third layer restores what an incident destroys. Endpoint backup protects files stored locally, while SaaS backup protects the OneDrive, SharePoint, Teams and Google Drive content that syncs to the device. If ransomware encrypts a synced folder, the encrypted versions replicate to the cloud, so recovery depends on an independent, immutable copy taken before the attack. This layer connects endpoint protection to broader cyber resilience planning.
Table 1. The Three-Layer Endpoint Protection Model
| Layer | Question It Answers | Core Tools | Primary Output |
|---|---|---|---|
| 1. Prevent and detect | Can we stop or catch the attack? | EPP, next-generation antivirus, EDR, XDR | Blocked threats, alerts, isolated devices |
| 2. Configure and prove | Are devices set up correctly, and can we show it? | UEM, Microsoft Intune, compliance baselines, patching | Compliance reports, drift alerts, audit evidence |
| 3. Recover | Can we restore data and devices after an incident? | Endpoint backup, SaaS backup, device reimaging | Restored files, mailboxes, sites and devices |
Core Capabilities Of An Endpoint Protection Platform (EPP)
An enterprise-grade endpoint protection platform typically includes the following capabilities:
- Next-generation antivirus (NGAV): Uses machine learning and behavioral analysis to block unknown malware, not only known signatures.
- Exploit and ransomware prevention: Stops memory exploits, script abuse and mass file encryption.
- Device encryption: Protects data at rest if a device is lost or stolen.
- Application control and patch management: Limits which software can run and closes known vulnerabilities.
- Device control and data loss prevention (DLP): Restricts USB storage, printing and uploads of sensitive files.
- Identity integration: Feeds device health into conditional access so risky devices cannot reach corporate apps.
- Centralized management: Applies policy, tracks agent coverage and reports status from one console.
EPP Vs. EDR Vs. XDR: How The Endpoint Security Stack Fits Together
EPP Vs. EDR: Prevention Vs. Investigation
EPP is preventive. It decides whether a file or process should run and blocks it if it looks malicious. Endpoint detection and response (EDR) is investigative. It assumes some attacks will bypass prevention, so it records activity, raises alerts on suspicious behavior and gives responders tools to hunt, contain and remediate threats. Many enterprise products now combine EPP and EDR in a single agent, but the functions remain distinct.
EDR Vs. XDR Vs. MDR
Extended detection and response (XDR) correlates endpoint telemetry with email, identity, network and cloud signals to give a wider view of an attack. Managed detection and response (MDR) is a service rather than a product: a provider's analysts monitor and respond using EDR or XDR tools on the customer's behalf.
Where Unified Endpoint Management (UEM) Fits
UEM tools such as Microsoft Intune enroll devices, push configuration profiles, deploy apps and enforce compliance policies across Windows, macOS, iOS and Android. UEM does not detect malware on its own, but it supplies the configuration and compliance layer that EPP and EDR depend on.
Table 2. Endpoint Security Approaches Compared
| Approach | What It Does | Scope | Primary Output |
|---|---|---|---|
| Antivirus | Blocks known malware using signatures | Individual devices | Quarantined files |
| EPP | Prevents known and unknown threats before execution | Managed endpoints | Blocked threats, policy status |
| EDR | Detects, investigates and contains active threats | Managed endpoints | Alerts, attack timelines, device isolation |
| XDR | Correlates signals across security domains | Endpoint, email, identity, network, cloud | Correlated incidents |
| MDR | Provides outsourced monitoring and response | Depends on the tools in use | Analyst-led response |
| UEM | Enrolls, configures and enforces device compliance | All enrolled devices | Compliance status, configuration profiles |
| Endpoint backup | Copies and restores device and synced SaaS data | Devices and cloud data | Recovery points, restored data |
Endpoint Protection For Microsoft 365 And Intune
In Microsoft environments, Microsoft Defender for Endpoint provides EPP and EDR, while Microsoft Intune provides UEM, compliance policies and security baselines. Conditional access in Microsoft Entra ID uses Intune compliance status to decide whether a device can open Microsoft 365 data.
Configuration Drift: Why Day-One Baselines Decay
Baselines degrade over time. Administrators create exceptions, users gain local admin rights, policies conflict and new devices enroll with incomplete profiles. In organizations that run multiple Microsoft 365 tenants, inconsistent policies across tenants compound the problem. Regular drift detection and correction, with a record of each change, keeps the compliance layer accurate and supports operational governance.
Why Wiping A Device Is Not Data Recovery
Remote wipe is a security control. It removes corporate data from a lost or compromised device, but it does not restore that data. Under the shared responsibility model, the customer remains accountable for its own information, including recovery from accidental deletion, malicious deletion and ransomware encryption that syncs back to OneDrive or SharePoint. Native retention features help, but they are not designed to serve as an independent, point-in-time cloud backup.
Endpoint Protection For AI Agents And AI PCs
AI changes both what runs on the endpoint and what it can do. Endpoint protection programs need to account for two shifts.
AI PCs And On-Device Models
AI PCs run language models locally on NPUs. Local inference keeps some data off the cloud, but it also creates new assets to protect, including model files, prompt histories, indexed screen content and local vector stores. Endpoint policies should define which local AI features are allowed, where their data is stored and whether it is encrypted.
AI Assistants And Agents Acting With User Permissions
AI assistants such as Microsoft 365 Copilot and autonomous agents increasingly take actions instead of only answering questions. An agent running on or from a device can read files, send messages and call APIs with the signed-in user's permissions or with its own non-human identity. That makes prompt injection a device-level risk, because hidden instructions in a document or webpage can direct an agent to exfiltrate data. Protecting AI on the endpoint requires an inventory of agents and their identities, least-privilege access, activity monitoring and the ability to roll back what an agent changed. These controls align with Zero Trust for AI and AI agent management practices.
Endpoint Security Best Practices
The following endpoint security best practices map to the three-layer model and to frameworks such as the NIST Cybersecurity Framework 2.0, CIS Controls and ISO/IEC 27001:
- Maintain a complete device inventory, including BYOD, servers, virtual machines and AI PCs.
- Deploy EPP and EDR on every supported endpoint, and track agent coverage as a metric.
- Enforce encryption, patching and secure configuration baselines through UEM.
- Detect and correct configuration drift, and keep an audit trail of every change.
- Tie device compliance to conditional access and phishing-resistant multifactor authentication.
- Apply least privilege to users, service accounts and AI agents.
- Back up endpoint and synced SaaS data to an immutable, isolated location, and test restores regularly.
- Measure coverage, drift rate, mean time to respond and recovery time, and report trends to leadership.
How AvePoint Completes Endpoint Protection
Endpoint protection is strongest when prevention, configuration and recovery work together. AvePoint is not an EPP or EDR vendor and does not replace Microsoft Defender or other detection tools. Instead, AvePoint completes the second and third layers of the model.
AvePoint Elements helps IT teams manage and secure users and devices at scale by enforcing Intune policies, encryption and compliance baselines, detecting and correcting drift, and producing audit-ready reports across tenants. That helps organizations turn policy into evidence auditors and boards accept. AvePoint Cloud Backup provides granular, immutable backup and restore for the Microsoft 365, Google Workspace and Salesforce data that syncs to every device, so teams can recover any asset, whether data, infrastructure or agent, when it matters.
Delivered on the AvePoint Confidence Platform from AvePoint, the AI Trust Company, these capabilities extend 25 years of data protection experience across your entire AI estate. The result: innovation scales without scaling risk, and enterprises can deploy AI with confidence.

Secure Every Endpoint With AvePoint
Standardize identity and device policies, monitor endpoint compliance and reduce configuration drift across Microsoft 365 tenants with AvePoint User & Device Management.
Frequently Asked Questions
Grace Harrison is a Product Marketing Manager at AvePoint, Inc., based in Jersey City, NJ. She works in the Product Strategy department, contributing to solutions like AvePoint Cloud Backup, AvePoint Fly, and AvePoint tyGraph. Grace plays a key role in developing marketing strategies and competitive intelligence to support AvePoint's field teams and enhance their selling tools.