
See Every AI Asset. Prove You're in Control.
Discover every model, agent, skill, and MCP server in your environment, secure how they touch sensitive data, and prove compliance with audit-ready evidence.
You Can't Govern What You Can't See.
Models. Agents. Skills. MCP servers. Every new AI capability your teams adopt is another asset touching sensitive data, and most of it never crosses a security or compliance review. AvePoint’s approach to AI Security and Governance gives you a single, unified inventory and policy layer across your entire AI estate, and the data it interacts with, so nothing operates in the dark.
Gartner's own research is direct about this:
"AI governance platforms that miss cybersecurity miss the point. Agentic risk gets the headlines, but models, skills, and the data behind them all carry their own exposure. AvePoint’s approach to AI Security & Governance is built to cover all of it, with complimentary compliance, risk, and operational management, across every type of AI asset in a unified solution."
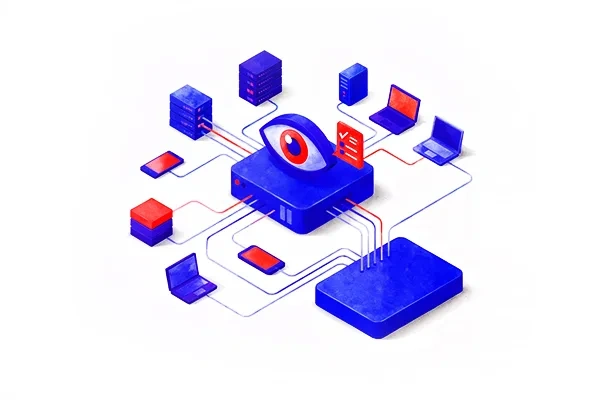
Discover & Inventory Every AI Asset
See every model, agent, skill, and MCP server running across Microsoft, Google, and third-party platforms, automatically, with no manual registration.
Secure How AI Touches Sensitive Data
Understand what data each AI asset can access, and enforce least-privilege at the asset level, not just the user level. Flag models, skills, and agents alike when they reach further into sensitive data than their purpose requires.
Enforce Governance Across the Full Lifecycle
Risk-tier every AI asset, assign ownership based on real usage, and manage each one from provisioning through decommission, so nothing outlives its purpose or its access by accident. High-risk assets can require human approval automatically with HITL and HOTL before consequential actions.
Prove Compliance with Audit-Ready Evidence
Produce audit-ready reports mapped to regulatory frameworks including SOC 2, GDPR, HIPAA, and emerging AI regulations, across your entire AI estate. For agents specifically, that includes the ability to back up and restore configurations to a known-good state after drift or compromise, an agent resilience capability no other governance vendor offers.
Governance and Security for the Whole AI Estate

No Gateway, No Bottleneck
AvePoint connects directly to the cloud platforms you own and governs not as a proxy sitting in your AI workloads' execution path. No added latency, no new failure points.

Built on Existing Trust
AvePoint already manages Microsoft 365 and Google Workspace governance for thousands of enterprises. Extending that trust across your AI estate isn't a new vendor relationship, it's the same governance and security always provided by AvePoint, now doing more.

Every AI Asset, One Governance Layer
Models, agents, skills, and MCP servers each carry their own risk. AvePoint governs and secures all of it from a single policy layer, so nothing gets missed. No more silos and fragmented security and operation solutions.

Get the AI Governance Readiness Checklist
A practical guide to validating ownership, security, and lifecycle controls across your models, agents, and skills before you scale further.
Your Questions, Answered
Know What Your AI Is Doing. Prove It, Too.
See every model, agent, skill, and MCP server in your environment in your first session. No manual setup required.