
Key Takeaways
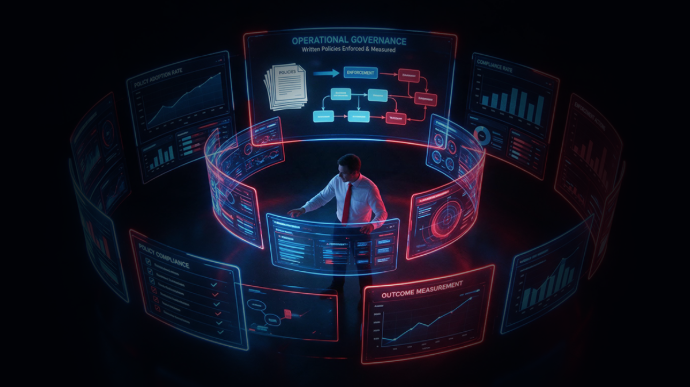
- Operational governance turns written policy into enforced, measured practice, which makes governance auditable rather than aspirational.
- It differs from corporate governance in scope: corporate governance sets direction and fiduciary oversight, while operational governance runs the daily machinery that proves direction is followed.
- A complete operational governance framework has five components: decision rights, policy translation, performance monitoring, risk and compliance management, and continuous improvement.
- The governance operating model (centralized, federated or hub-and-spoke) and a clear committee structure decide which body owns each choice and who oversees operational risk.
- AI operational governance applies the same discipline at machine speed, where autonomous agents demand continuous, evidence-based control instead of periodic review.
Most organizations do not fail at governance because they lack policies. They fail because those policies never become daily practice. Operational governance closes that gap. It is the discipline that turns written standards into decisions people make, controls systems enforce and evidence auditors accept. This guide explains what operational governance is, how it differs from corporate governance and how to run it across a modern AI estate.
What Is Operational Governance?
Operational governance is the discipline of turning written policy into enforced, measured, everyday practice. It defines who decides what, translates standards into automated controls, monitors performance against clear thresholds and captures evidence continuously. Where corporate governance sets direction, operational governance runs the machinery that proves that direction is being followed. That single distinction is what makes it auditable rather than aspirational.
The concept is broader than process management because it ties decision authority to technical enforcement and traceability. In practice, operational governance spans approvals, logging, review cadences, escalation paths and control ownership. It is the layer where a policy stops being a document and becomes a control that runs, produces a record and can be inspected later.
The Short Definition Of Operational Governance
In one line: operational governance is how governance actually runs. It answers four operational questions for every rule an organization sets. Who approves the action? Who sets the policy behind it? Who reviews exceptions? And who reports the outcome to leadership? When those answers are explicit, enforced and evidenced, governance is operational. When they live only in a slide deck, it is not.
Governance On Paper Versus Governance In Practice
The most common failure mode is "governance theatre": committees meet, status is reviewed and concerns are raised, but no decision is recorded and no control changes. Teams can describe a control yet cannot prove it runs consistently in production. Mature AI governance avoids this trap by binding every policy to an enforcement point and a durable record, so the standard on paper and the behavior in the system are the same thing.
Operational Governance Model: Scope, Owner, Cadence, Evidence
The table below summarizes how operational governance sits alongside the governance types it depends on. Read it top to bottom as a chain: direction is set, technology is aligned, inputs and outputs are controlled, and operational governance makes all of it happen in practice.
| Governance Type | Primary Question | Owner | Cadence | Success Metric |
|---|---|---|---|---|
| Corporate governance | Are we heading the right way? | Board | Quarterly | Fiduciary trust |
| IT governance | Does technology fit strategy? | Executive / CIO | Monthly | Investment return |
| Data and AI governance | Can we trust the inputs and outputs? | CDO / CAIO | Continuous | Data and model integrity |
| Operational governance | Is the policy actually enforced and evidenced? | Process owners | Daily to continuous | Audit-ready evidence |
Operational Governance vs Corporate Governance
Corporate governance and operational governance are two layers of the same system. Corporate governance defines the rules, responsibilities and accountability structures at the board and executive level. Operational governance translates those principles into the day-to-day processes, controls and evidence that keep the organization running inside its obligations. One sets intent. The other proves execution.
How Operational Governance And Corporate Governance Work Together
At the corporate level, governance operates through board oversight, executive accountability and formal policy approval. It answers who holds authority and what values guide the organization. Operational governance is where those decisions become action: how incidents are handled, how access is granted, how standards are maintained and how each of those is recorded. In regulated environments, operational governance is the layer auditors and regulators scrutinize most, because it is where intent is either demonstrated or exposed as a gap.
Operational Governance vs IT And Data Governance
Corporate governance is not the only neighbor worth distinguishing. IT governance aligns technology investment to strategy and answers whether the organization is spending on the right systems. Data and AI governance controls the quality, access and lineage of the inputs and outputs those systems consume and produce. Operational governance is the connective tissue: it takes the direction from corporate governance, the priorities from IT governance and the controls from data governance, then makes sure all three are enforced and evidenced in daily work. Without it, each discipline produces sound policy that no one can prove is being followed.

See governance run in practice
AvePoint helps enterprises move from policy on paper to policy enforced across every cloud, with command centers that see and shape behavior.
The Operational Governance Framework: Five Core Components
An operational governance framework is the repeatable structure that converts strategy into controlled daily activity. Five components appear in every durable version of it. Together they form a loop: rights are assigned, policy is enforced, performance is watched, risk is escalated and findings feed improvement.
Decision Rights: A Decision Rights Framework That Holds Up Under Audit
Effective operational governance is largely a matter of decision rights: who decides what, with what authority, accountable to whom. A decision rights framework names, for each material choice, which function is responsible, which is accountable, which is consulted and which is informed. The traceability test is simple. For any past decision, can you show who decided, who was consulted and who accepted the risk? If yes, the framework holds under audit. If not, you have an org chart, not governance.
Policy Translation: Turning Written Standards Into Enforced Controls
A policy that cannot be enforced is a suggestion. Policy translation is the work of converting each written standard into an automated control with a defined owner and a captured record. This is the same rigor that AI model governance applies to non-agent AI risk, and that AI data governance applies across Microsoft, Google and Salesforce. The goal is one control plane and one source of truth, so a standard is enforced the same way everywhere it applies.
Performance Monitoring, Risk And Continuous Improvement
The remaining three components keep the loop alive. Performance monitoring measures operations against defined metrics, service level agreements and thresholds, so drift is visible early. Risk and compliance management sets escalation paths and requires explicit, recorded risk acceptance rather than silent exceptions. Continuous improvement closes the loop by feeding audit findings and near-misses back into updated controls. Skip any one of the three and governance quietly reverts to theatre.
The Three Levels Of Operational Governance
Operational governance runs at three levels, and most dysfunction comes from blurring them. Each level has an appropriate scope, an appropriate speed and an appropriate kind of decision. When the levels are clear, decisions move quickly and land at the right altitude. When they collapse into one another, boards get pulled into operational detail and frontline teams wait on choices they were equipped to make.
Board Level: Risk Acceptance And Material Oversight
The board provides fiduciary oversight, evaluates material investments and accepts risk that crosses the organization's stated appetite. It does not approve individual changes. Its job is to confirm that a governance system exists, that it works and that the residual risk it produces is understood and owned at the top.
Executive Level: Portfolio Decisions And Escalation Resolution
Executives set strategy into portfolio decisions, resolve escalations the operational level cannot settle and allocate the resources governance needs to function. This is where firefighting turns into steering. The executive level also owns the minimum standards that federated or hub-and-spoke operating models push down into the business.
Operational Level: Day-To-Day Decisions Within Delegated Authority
The operational level makes day-to-day decisions inside delegated authority: architecture reviews, change approvals and the routine choices that keep work moving. Most decisions should resolve here. If nearly everything is escalated, the operating model has failed to delegate, and governance becomes a queue rather than a system.
The Governance Operating Model and Committee Structure
A governance operating model is the bridge between governance strategy and daily execution. It defines governance bodies, roles, decision rights, escalation paths and the processes that connect them. Two organizations can adopt the same framework and get very different results, because the operating model, not the framework, decides whether governance is fast and clear or slow and blurred.
Centralized, Federated And Hub-And-Spoke Operating Models
Most organizations converge on one of three archetypes. A centralized model puts one function in charge of every decision, which gives consistent policy but a slow approval queue, and it suits early adoption. A federated model pushes decision rights into business units under central minimum standards, which scales well but risks policy drift. A hub-and-spoke model keeps policy and audit central while delegating route-level approvals to embedded governance leads, which balances consistency with speed. The right choice depends on scale, maturity and how much variation the organization can safely tolerate.
Which Governance Body Oversees Operational Risk?
Operational risk oversight usually follows the three lines of defense. Business line management owns and treats risk in the first line, risk and compliance functions set and monitor policy in the second line, and internal audit plus the board provide independent assurance in the third. At board level, oversight is typically delegated to a committee. In a Deloitte and Center for Audit Quality survey of audit committee members, 58% said the audit committee holds primary oversight of cybersecurity risk, while 25% said the full board does, a useful signal of how operational and technology risk is escalated in practice.
For boards weighing model and system exposure specifically, AI model risk management offers a board-level framing that pairs naturally with the committee structure described here.
What Is AI Operational Governance?
AI operational governance is operational governance applied to AI systems: the discipline of enforcing, measuring and evidencing policy for the models and agents an organization runs. It matters because AI changes the assumptions traditional governance was built on. Systems no longer behave predictably, follow fixed rules and wait for human execution. They act autonomously, at machine speed, across interconnected systems.
Why AI Breaks Traditional Operational Governance
Periodic review cannot govern continuous, machine-speed decisions. Committees meet monthly, but agents act thousands of times a day, so governance has to move from static controls to continuous oversight. The urgency is widely felt: in PwC's 2025 Responsible AI Survey, 87% of leaders said they expect AI agents to reshape governance within the next year. Three shifts drive the pressure: decisions happen faster than committees can convene, delegated authority becomes literal when an agent acts on its own, and models and data change continuously while written policy stays still.
How Does BPMS Governance Reduce Operational Risk?
Business process management system (BPMS) governance reduces operational risk by embedding controls directly into the workflow rather than bolting them on afterward. When approvals, segregation of duties, logging and exception handling are enforced inside the process engine, risky steps cannot be skipped and every action leaves a record. That is the same principle behind CloudOps and cyber resilience: governance is strongest when it is built into how the system runs, so control and evidence are automatic instead of manual.
The Operational Governance Maturity Curve: From Ad Hoc To Autonomous
Operational governance is not binary. Organizations progress along a maturity curve, and knowing where you sit tells you what to fix next. The five levels below move from decisions made informally to governance that runs continuously and evidences itself. Most enterprises sit at level two or three and stall there, because the jump to enforced and measured governance requires automation their tooling does not yet provide.
- Level 1, Ad Hoc: decisions are made informally and leave no record. Governance depends on the loudest voice in the room.
- Level 2, Documented: policy exists on paper, but enforcement is manual and inconsistent. Teams can describe controls they cannot prove.
- Level 3, Enforced: controls are automated and applied consistently. The standard and the system behavior finally match.
- Level 4, Measured: governance outcomes are instrumented, so effectiveness is tracked with metrics rather than assumed.
- Level 5, Autonomous: governance is continuous and self-evidencing, producing audit-ready records without a manual scramble.
The curve is also a roadmap. If you cannot prove a control runs in production, your first move is level three, not a new policy. If you can enforce but cannot measure, level four is the priority. Naming the level turns a vague sense that governance is weak into a specific, fundable next step.
Operational Governance Best Practices
Operational governance best practices share one theme: make the standard, the control and the evidence the same thing. The checklist below distills what separates governance that holds up under audit from governance that only looks good in a report.
- Assign explicit decision rights for every material choice, then test them against the traceability question: who decided, who was consulted, who accepted the risk?
- Translate each written policy into an automated control with a named owner, so enforcement does not depend on memory or goodwill.
- Instrument metrics and capture evidence continuously, rather than reconstructing it before an audit.
- Run a clear cadence: daily for stability, weekly for coordination, monthly for structural review and quarterly for strategic reassessment.
- Require explicit, recorded risk acceptance for exceptions, and feed every finding back into the next version of the control.
- Measure outcomes, not activity, because counting meetings held guarantees drift while measuring decisions evidenced does not.
Common Operational Governance Mistakes And How To Avoid Them
The failure patterns in operational governance are consistent across industries, which makes them easy to anticipate. Each one shares a root cause: a gap between what governance claims and what the system can prove. The four below account for most audit findings.
- Governance theatre. Committees meet and review status but record no decisions and change no controls. Fix it by requiring every meeting to produce a decision, an owner and a date.
- Decision rights on an org chart only. Authority is named but never binds to a control, so decisions are unenforced. Fix it by connecting each right to an enforcement point in the system.
- Measuring activity instead of outcomes. Counting meetings held or policies written guarantees drift. Fix it by tracking decisions evidenced and controls proven, not effort expended.
- Static governance over dynamic systems. Periodic review cannot keep pace with AI and automation. Fix it by moving enforcement and evidence into the workflow, where they run continuously.
How AvePoint Operationalizes Governance Across Your Entire AI Estate
Operational governance is only as strong as the plane it runs on. When policy is enforced differently in each cloud and evidence is scattered across tools, governance stays aspirational no matter how good the framework looks on paper. AvePoint is the unifying Trust Layer for AI, and it exists to remove exactly that gap.
As the unifying Trust Layer for AI, AvePoint helps more than 28,000 organizations and 6,000 channel partners protect, secure and govern their entire AI estate across data, infrastructure, AI and agents for Microsoft, Google, Salesforce and other leading cloud environments. For operational governance specifically, that means one place to assign decision rights, enforce policy as automated guardrails, monitor behavior and capture the immutable, audit-ready evidence that turns policy into evidence auditors and boards accept.
The business value is direct. Decision rights become traceable, controls become consistent across clouds, and evidence becomes continuous instead of a fire drill before every audit. That is how innovation scales without scaling risk, so enterprises can deploy AI with confidence.
Make your operational governance auditable, not aspirational
Turn policy into evidence across your entire AI estate with one control plane and one source of truth on the AvePoint Confidence Platform.
Frequently Asked Questions
Timothy Boettcher is a senior go-to-market and product marketing leader and Microsoft MVP for M365 Copilot, specializing in enterprise AI, data governance, and adoption strategy across global markets. He is known for translating complex technology into clear, trusted narratives that help leaders make confident decisions and drive responsible AI adoption at scale.